Attacker drains 114 ETH from Aave users through flawed third-party adapter
A flaw in a third-party lending adapter built on top of Aave v3 let an attacker drain roughly 114 ETH, worth more than $300,000, from two compromised Safe multisig wallets on October 2. Aave’s own smart contracts were untouched, but the episode is a reminder for institutional users that protocol-level security audits do not cover every integration layered on top of a lending market.
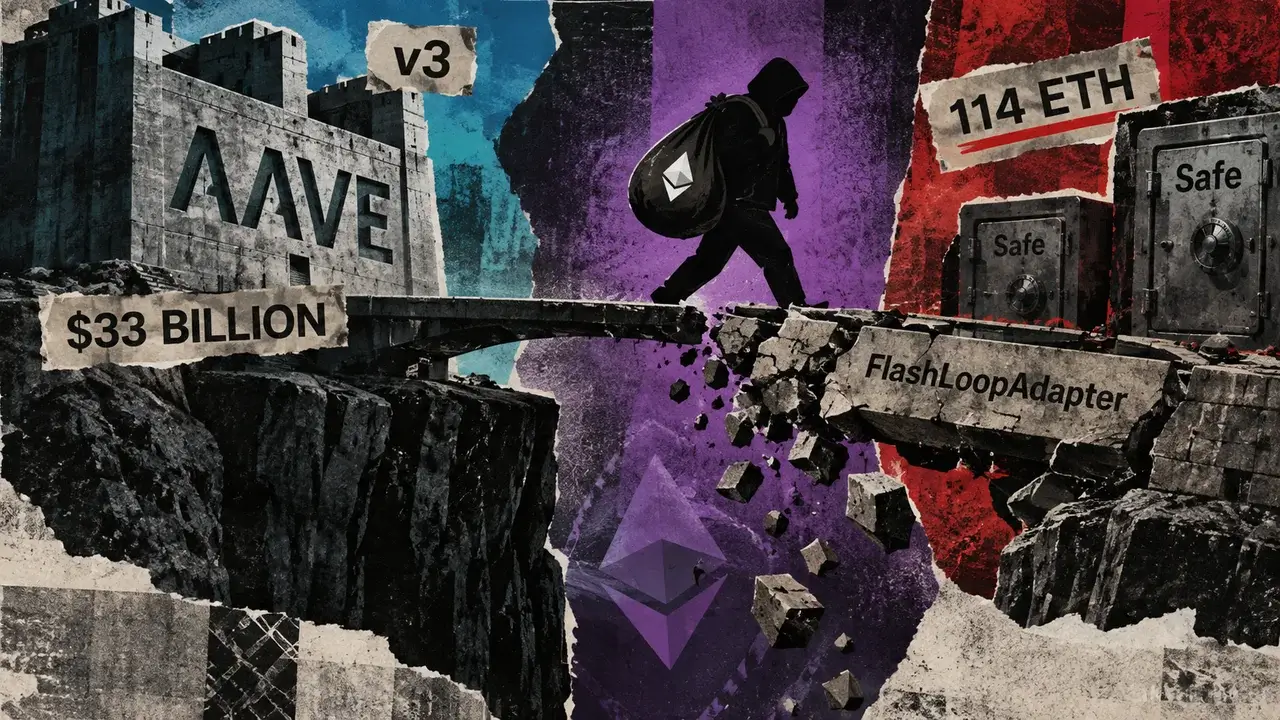
- SlowMist estimated the direct loss at about 114.09 ETH drained from two Safe multisig wallets.
- The attacker also triggered repayment of roughly 1,300 WETH in debt to unlock collateral tied to Aave v3 positions.
- Aave founder Stani Kulechov said the exploit involved a third-party external adapter, not the Aave v3 contract itself.
- 114 ETH direct loss stolen, valued at over $300,000
- $33B Aave total value locked, the largest of any DeFi lending protocol
- 1,300 WETH debt repaid by the attacker to free collateral
Blockchain security firm SlowMist said the attacker compromised two Safe multisig wallets through a flaw in the FlashLoopAdapter, a helper contract that lets users batch flash-loan style operations against Aave v3 positions without touching the core protocol directly. The adapter’s authentication checks could be bypassed, SlowMist said in a post on X, allowing arbitrary calls that drained collateral from the affected wallets. The firm’s findings were first detailed in a report by CryptoSlate.
SlowMist Traces the Bug to a Forged Safe Module Check
SlowMist pinned the vulnerability to the adapter’s open() and close() functions, which verify whether a calling Safe wallet has enabled the FlashLoopAdapter as an active module. That verification step could be spoofed.
The attacker built a fake Safe contract that always returned a positive response to the module check. The adapter accepted the forged authentication and moved on to its internal swap logic.
The more consequential flaw let the caller specify both the router address and the calldata for an external contract call inside that swap function. The attacker pointed the router back at the victim’s real Safe wallet and supplied instructions invoking Safe’s execTransactionFromModule function.
Because the FlashLoopAdapter was already enabled as a legitimate module on the affected wallets, that single call gave the attacker a direct path to execute transactions through the victims’ Safes, withdrawing weETH and other collateral tied to their Aave positions.
Kulechov Says Core Aave v3 Contracts Had Zero Exposure
Aave founder Stani Kulechov moved quickly to separate the incident from the protocol itself, stressing that the adapter sits outside Aave’s audited contract set.
This is not Aave v3 contract, it’s third party external adapter built on top of Aave, zero effect on Aave v3.
Stani Kulechov, founder, Aave
The distinction matters for a protocol holding more than $33 billion in total value locked, making it the largest decentralized lending market by that measure. Aave governance has spent recent months vetting new infrastructure layered around the core protocol, from a proposal to review the Sentora hub-and-spoke lending framework for V4 to accepting seven Coinbase tokenized stocks as Base collateral, and each addition widens the surface that sits outside the core contract’s own audit history.
Unanswered: Which Other Wallets Enabled the Same Module
SlowMist’s disclosure leaves open whether other Safe wallets beyond the two confirmed victims had enabled the FlashLoopAdapter as a module, and whether the adapter’s developers have identified further exposed positions. Neither the adapter’s team nor SlowMist has published a full list of affected addresses as of this writing.
Aave has previously shown it is willing to act preemptively on integration risk rather than wait for an exploit, as when the Arbitrum Security Council halted new Stylus contracts over AI attack risk. Whether a similar freeze applies to third-party adapters remains an open question for Aave governance.
The CCS read. This loss is small against Aave’s $33 billion in deposits, but it is the kind of headline that gets conflated with protocol risk by investors who do not distinguish a core contract from a third-party wrapper. Institutional allocators sizing exposure to Aave should be pricing the audit status of every adapter they route through, not just the base protocol’s own track record.
SlowMist has not said whether it is coordinating with the FlashLoopAdapter’s developers on a patch or disclosure timeline, and no public tally yet exists of how many other Safe wallets still have the vulnerable module enabled.