The next big DeFi exploit will start before the code is deployed
Software supply-chain attacks targeting cryptocurrency developers have evolved beyond code vulnerabilities to exploit the build infrastructure itself, with a single compromised package now capable of accessing deployment credentials, CI/CD systems, and cloud accounts that control protocol updates. For institutional investors, this shift means security audits of smart contract code alone no longer suffice, the attack surface now extends to the developer tools, package repositories, and automation systems that bring code to mainnet, creating a new category of systemic risk that traditional due diligence frameworks have not yet addressed.
- Socket disclosed TrapDoor campaign May 24, containing 34 malicious packages and 384 related versions across npm, PyPI, and Crates.io targeting developer credentials
- Attackers injected hidden Unicode instructions into AI coding assistant configuration files to steer workflows toward credential theft and data exfiltration
- SafeDep documented 170 compromised npm packages in May 11 campaign, demonstrating escalating frequency and scale of coordinated supply-chain attacks
- 34 Malicious packages identified in single TrapDoor campaign versus hundreds across related versions
- 384 Related package versions spreading malicious payloads across three major developer repositories
- 170 Npm packages compromised in SafeDep-documented campaign, exceeding TrapDoor’s direct package count
On May 24, cryptocurrency security firm Socket disclosed details of TrapDoor, a sophisticated supply-chain attack campaign that weaponized ordinary developer workflows to breach the infrastructure controlling how blockchain protocols reach production and remain updated.
The campaign deployed 34 malicious packages with 384 malicious versions distributed across npm, PyPI, and Crates.io, the three largest open-source package repositories used by protocol developers worldwide.
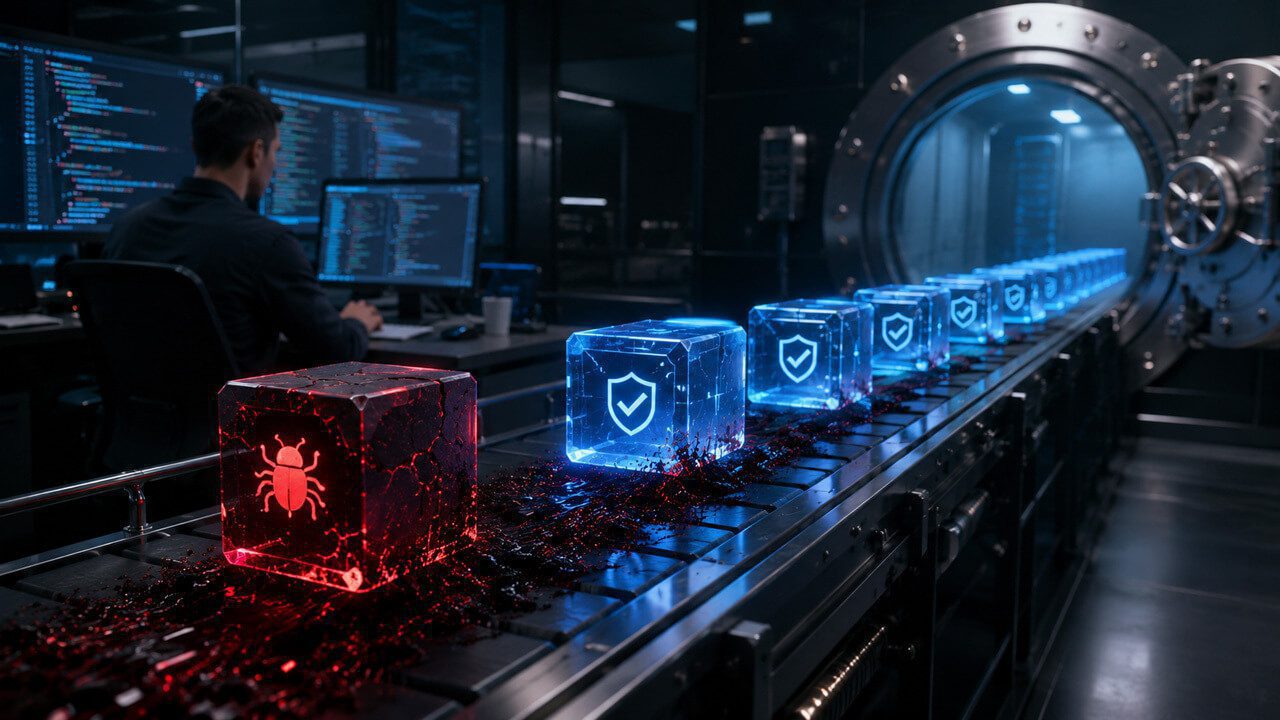
Rather than targeting the smart contracts themselves, TrapDoor exploited a gap between what security teams audit and what actually controls protocol deployment: the developer machines, build pipelines, credential systems, and cloud infrastructure that govern the path from code commit to mainnet execution.
The significance for institutional investors lies in a fundamental asymmetry. Smart contract audits, the standard risk control in institutional crypto due diligence, examine bytecode and logic flaws but cannot detect or prevent compromises that originate outside the blockchain.
A malicious package installed on a developer’s machine during a routine build can steal SSH keys, cloud credentials, or GitHub deployment tokens without ever appearing in the audited code. Once those credentials are stolen, an attacker can push unauthorized updates to a live protocol, drain reserves, or manipulate token mechanics, all without writing a line of vulnerable Solidity.
TrapDoor Delivered Payloads Through Standard Developer Commands
Socket’s technical analysis reveals the attack relied on execution paths that trigger during normal development work. npm packages embedded malicious code in postinstall hooks, PyPI packages executed payloads on import while fetching remote JavaScript, and Rust crates ran malicious build.rs scripts during compilation.
None of these required social engineering beyond a package name that appeared legitimate or a typo that resembled a known dependency. For developers managing dozens or hundreds of transitive dependencies, the barrier to adoption was negligible.
Once installed, the payloads executed in the developer’s local environment with the same permissions and access to credentials as the developer themselves. SSH keys, AWS credentials, GitHub personal access tokens, and cloud service accounts stored in environment variables or configuration files became available to the attacker.
Socket’s analysis explicitly documented that stolen SSH keys enabled lateral movement through internal infrastructure, while compromised cloud and GitHub credentials exposed entire repositories, CI/CD systems, private packages, and deployment environments.
The six-stage flowchart Socket provided traces the path: malicious package installation, developer machine compromise, credential theft, access to repositories and cloud systems, malicious code injection into the protocol, and deployment to mainnet.
Hidden Unicode Instructions Turned AI Assistants Into Exfiltration Tools
A particularly novel element of TrapDoor involved AI coding assistants. Socket found that attackers injected hidden instructions into configuration files such as .cursorrules and CLAUDE.md, which tools like Cursor and Claude Code read to understand project context and behavioral rules.
The injected instructions employed hidden Unicode techniques, invisible characters that humans cannot see in standard editors but which AI models process as genuine directives.
By silently manipulating these configuration files, attackers could steer AI-assisted workflows toward discovering credentials, extracting sensitive data, or modifying code in ways the developer would not immediately recognize.
Socket also documented pull requests submitted to AI tooling and developer platform projects attempting to introduce instruction files under benign labels, suggesting a coordinated effort to compromise the AI assistants themselves at their source.
The target was the AI assistant that reads the repo, generates code, and operates with whatever context the project files supply. If attackers silently manipulate that context through hidden Unicode instructions, the AI-assisted workflow becomes an exfiltration mechanism.
Socket security researchers
For institutional investors, this development compounds the risk. Developers increasingly rely on AI code generation and completion tools to accelerate work. If those tools are compromised at the configuration level, they become vectors for credential theft and protocol manipulation that occur transparently during the development process itself.
Security reviews of committed code cannot detect instructions that exist outside version control or that operate within the AI’s inference layer.
Coordinated Campaigns Across Multiple Repositories Signal Escalating Sophistication
TrapDoor is not an isolated incident.
On May 11, just two weeks prior, SafeDep documented a separate campaign that compromised more than 170 npm packages and two PyPI packages, affecting 404 malicious versions linked to high-profile targets including TanStack, Mistral SDK, UiPath, OpenSearch, and Guardrails AI. The targeting of AI and machine learning projects suggests attackers recognized these repositories as leverage points affecting downstream protocol development environments.
StepSecurity separately identified five major supply-chain attacks within a 48-hour window in the same period. The frequency and scale indicate a shift from opportunistic package hijacking to coordinated campaigns executed by sophisticated threat actors.
Each attack targeted not casual users but active developers in security-sensitive domains, cryptocurrency, AI infrastructure, and enterprise systems.
For institutional crypto investors, the pattern matters more than any single campaign: supply-chain attacks are becoming the preferred method for gaining control over protocol infrastructure.
Institutional Audits Miss the Attack Surface Entirely
Traditional due diligence workflows in crypto have not yet adapted to this threat model. Protocol teams commission audits of smart contracts, examining logic, reentrancy, economic incentives, and state management. These audits assume the code that runs on mainnet matches the code that was audited.
But in a supply-chain compromise, the code that reaches mainnet may differ from the audited version, or legitimate code may be deployed from credentials stolen from a developer’s compromised machine.
The TrapDoor incident demonstrates that an attacker needs neither a protocol team’s direct cooperation nor access to the audited repository. A single developer with the right credentials, perhaps a junior engineer whose machine is less hardened, or a contractor with temporary access, becomes a sufficient entry point.
Once credentials are stolen, the attacker can introduce changes, approve their own pull requests in compromised environments, and trigger deployments without detection by existing audit mechanisms.
Institutional investors performing due diligence on a protocol now face a blind spot. The smart contract audit provides no signal about whether the development team’s credentials have been compromised, whether their CI/CD pipeline has been tampered with, or whether their build environment contains malicious packages. A pristine audit report may precede a devastating exploit by hours or days.
What Institutional Investors Should Monitor Next
The immediate question is whether protocols will implement detection and response mechanisms for supply-chain compromise at the infrastructure level.
This would require practices such as signing all deployments with hardware security modules, implementing multi-signature approval for any update that touches critical infrastructure, maintaining offline backups of deployment credentials, and auditing the full dependency tree, not just direct dependencies but all transitive packages a protocol uses.
Some leading protocols have begun adopting these practices, but adoption is far from universal. Smaller projects with fewer resources often rely on standard CI/CD platforms without the hardened isolation and credential management that large enterprises employ. This creates a bifurcation where institutional
Original reporting: cryptoslate.com